


'Malicious Intent': OpenAI CFO Warns Companies Against 'Cheap Chinese AI Models' Due To Safety Risks
And there it is...
OpenAI Chief Financial Officer Sarah Friar warned businesses on Wednesday that adopting low-cost Chinese artificial intelligence models carries material cybersecurity risks, telling Bloomberg that firms should prioritize Western models "on the cyber front."
"We think you want to be on more Western models, frankly."
— Bloomberg (@business) October 14, 2026
Businesses opting to use low-cost Chinese AI models are taking a cybersecurity risk, OpenAI CFO Sarah Friar tells @TomMackenzieTV https://t.co/example
Speaking at the International AI Summit in Dublin during Ireland's EU Council Presidency, Friar said companies embracing Chinese models need to weigh "the safety and security elements." The comments, part of a Bloomberg exclusive, echoed longstanding concerns from Anthropic and arrive as Chinese open-weight models continue to gain enterprise traction on cost and accessibility.
Friar also said the company is holding back a next-generation model - more capable than its GPT-6 Astra system - that OpenAI says produced a proof of the Navier-Stokes Millennium Prize problem and hundreds of other math proofs in recent weeks, as we detailed last week. Release is delayed pending further safety and alignment work. "We hold back sometimes, so we talk about pacing the frontier," she said in related summit remarks. She separately flagged that Chinese models are "getting very good from a cyber perspective" and are often open-source or open-weight, meaning "the folks with malicious intent have the tools."
The warning lands amid intensifying competition. Chinese labs have released a rapid succession of capable open-weight systems that rank near the top of various intelligence and cyber benchmarks while undercutting U.S. frontier pricing. OpenAI, Anthropic, and others have repeatedly alleged industrial-scale distillation campaigns in which Chinese developers extract reasoning from closed U.S. models to accelerate their own systems. Anthropic announced this week that new safeguards reduced such extraction by roughly 90-99 percent and specifically cited Z.ai (Zhipu) activity tied to its GLM-5.3 development.
OpenAI slashed token prices in half when the Chinese open model flood hit, and sparked the July chip rout. It then delayed its IPO. Now, Anthropic token prices have also been cut by 50% in the past month (still higher than OpenAI). Where's the bottom? https://t.co/HAVSREuH1D
— zerohedge (@zerohedge) October 14, 2026
Amodei and the Safety-Competition Blur
Anthropic CEO Dario Amodei has been the most consistent public voice framing Chinese AI progress as both a commercial and national-security problem. His September essay calling for frontier labs to deliberately slow capability advances placed China at the center of the argument: any democratic slowdown must be bounded by the size of the existing U.S. lead, paired with tighter advanced-chip export controls and aggressive measures against distillation and weight theft. Amodei has described a Chinese lead as posing "grave danger" and has warned of scenarios in which advanced agents could enable large-scale cyber damage or autonomous systems that outpace oversight.
Anthropic's own red-team work has highlighted the concrete risk differential. Testing of Z.ai's open-weight GLM-5.3 found exploit-generation performance close to Anthropic's restricted Claude Mythos Preview, yet with far weaker refusal and safety layers that could be bypassed with simple techniques. Because the weights are freely downloadable, the company argued, the model's capabilities are available to any actor without the access controls applied to closed frontier systems. Amodei has stopped short of calling for outright bans on open-weight models, instead advocating pre-release safety testing for highly capable systems regardless of open or closed status, alongside measures to keep advanced chips and large-scale distillation out of authoritarian hands.
Critics note the commercial overlay. Closed U.S. labs face direct competition from lower-cost Chinese open models that have captured significant token share on platforms such as OpenRouter. Warnings that emphasize "safety and security" simultaneously justify restrictions that protect market position. China's state-backed Global Times dismissed Amodei's essay as a "Cold War playbook."
Schmidt's Earlier Kinetic Warning
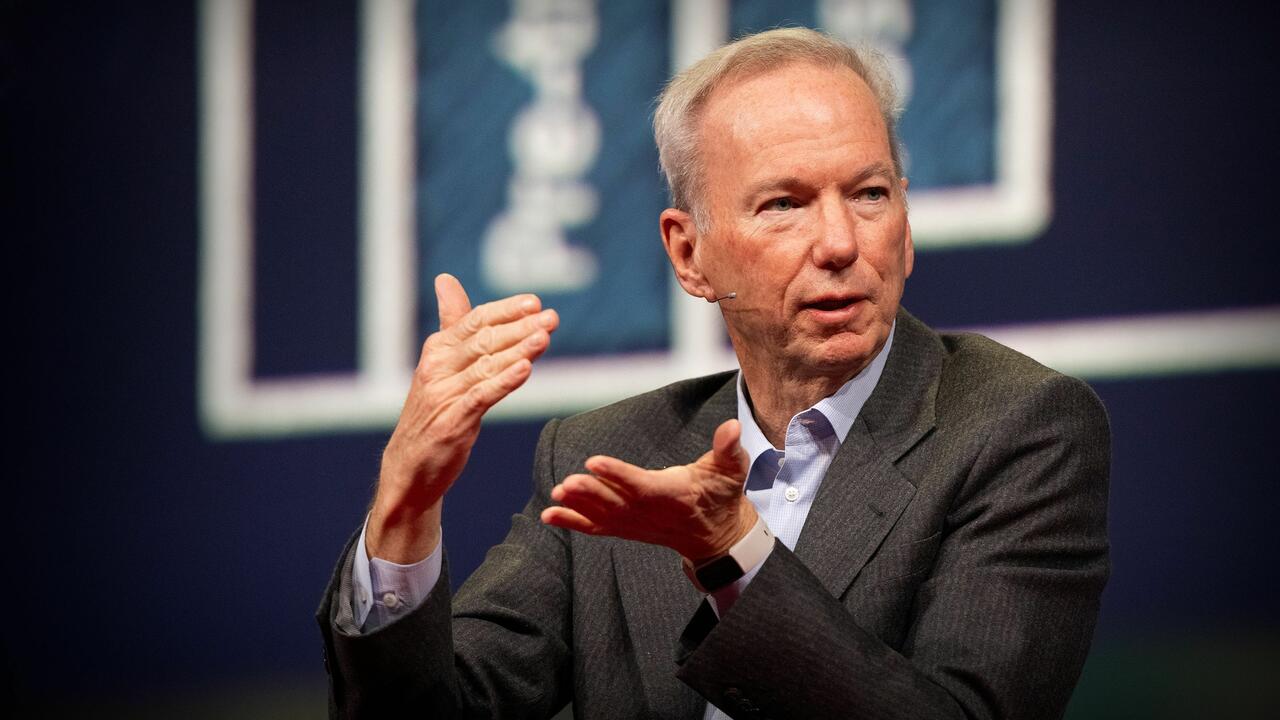
Former Google CEO Eric Schmidt offered a more stark geopolitical framing last year. In a May 2025 TED talk we covered, Schmidt role-played the incentives of a nation falling behind in the AI race. After failed attempts at code theft, human infiltration, and model sabotage, he posed the next step: "What's my next choice? Bomb your data center." He stated that conversations along these lines are already occurring among nuclear-armed states and that policymakers lack an adequate framework for the risks of a decisive AI lead.
The remarks aligned with the March 2025 "Superintelligence Strategy" paper Schmidt co-authored with then-Scale AI CEO Alexandr Wang and the Center for AI Safety's Dan Hendrycks. That paper introduced "Mutual Assured AI Malfunction" (MAIM) - a deterrence concept modeled on nuclear mutual assured destruction in which aggressive bids for unilateral AI dominance would be met with preventive sabotage, ranging from covert disruption of training runs to potential kinetic strikes on data centers and supporting infrastructure. The authors argued against a pure "Manhattan Project" race for superintelligence precisely because rivals would not passively accept a permanent imbalance.